

An Azure landing zone is the governed foundation you set up in Azure before workloads arrive. Microsoft defines it as "a proven and flexible architecture for governing, securing, and scaling a multi-subscription Azure environment." It decides identity, networking, policy, cost control and monitoring once, so every workload inherits the same guardrails instead of rebuilding them.
The reason it matters is ordering. Subscription structure, IP address space, naming and tagging are cheap to set up first and very expensive to change once workloads depend on them. This guide explains what a landing zone contains, Microsoft's eight design areas, the reference architecture, how to build one with Azure Verified Modules, and the mistakes that are hardest to undo.
What Is an Azure Landing Zone?
According to Microsoft's Cloud Adoption Framework, an Azure landing zone has two components:
-
Platform landing zone: the centralized foundation that establishes governance, security and shared resources for all workloads. Microsoft notes that most organizations should have only one platform landing zone per Microsoft Entra tenant.
-
Workload landing zones: the environments where workload teams deploy and operate their applications inside the guardrails the platform provides.
Three common misunderstandings:
-
It is not a single subscription. A landing zone spans a management group hierarchy and many subscriptions.
-
It is not a product you buy. It is an architecture, deployed with Microsoft's accelerators or your own infrastructure as code.
-
It is not only for large enterprises. Smaller organizations can start with a simplified version and add structure as they grow.
What Goes Wrong Without a Landing Zone?
Nothing breaks on day one. A team creates a subscription to move fast. Nobody enforces tags, so six months later costs cannot be attributed. A test port stays open. Data lands in an unapproved region and only surfaces during an audit. Broad permissions are granted because it was faster. Each issue is small; together they become technical debt that slows every new project, makes compliance evidence a manual exercise, and blocks safe adoption of Microsoft Fabric, Power BI and Copilot, which all assume governed identity and data.
Explore Azure Migration Services
How It Works: The 8 Design Areas
Microsoft organizes landing zone design into eight design areas in two groups:
|
Group |
Design area |
What it decides |
|---|---|---|
|
Environment (decide early, hard to change) |
Azure billing and tenant |
Tenant, enrollment and billing structure |
|
Identity and access management |
Authentication, authorization and privileged access |
|
|
Resource organization |
Management groups, subscriptions, naming and tagging |
|
|
Network topology and connectivity |
Hub and spoke or Virtual WAN, IP ranges, hybrid links, DNS |
|
|
Compliance (set up early, refine continuously) |
Security |
Controls, encryption, threat protection and secrets |
|
Management |
Monitoring, logging, backup and patching |
|
|
Governance |
Policy enforcement, cost control and compliance |
|
|
Platform automation and DevOps |
Infrastructure as code and deployment pipelines |
Microsoft also defines five design principles: subscription democratization, policy-driven governance, a single control and management plane, an application-centric service model, and alignment with Azure-native design and roadmaps. In practice they mean: hand subscriptions to teams, enforce guardrails with Azure Policy, avoid custom portals that wrap Azure, and prefer native services.
Platform Landing Zone vs Workload Landing Zone
|
Factor |
Platform landing zone |
Workload landing zone |
|---|---|---|
|
Purpose |
Shared foundation: governance, security, connectivity, management |
Where an application or workload runs |
|
Owner |
Central platform or cloud team |
Workload or application team |
|
Typical contents |
Management group hierarchy, hub network, firewall, Log Analytics, identity services |
Workload subscriptions, spoke virtual networks, app resources |
|
How many |
Usually one per Microsoft Entra tenant |
One per workload, often with dev, test and production environments |
|
Change pace |
Slow and controlled |
Frequent, within guardrails |
When this boundary is clear, onboarding a new workload is routine. When it is blurred, every new application becomes a negotiation.
Reference Architecture Example
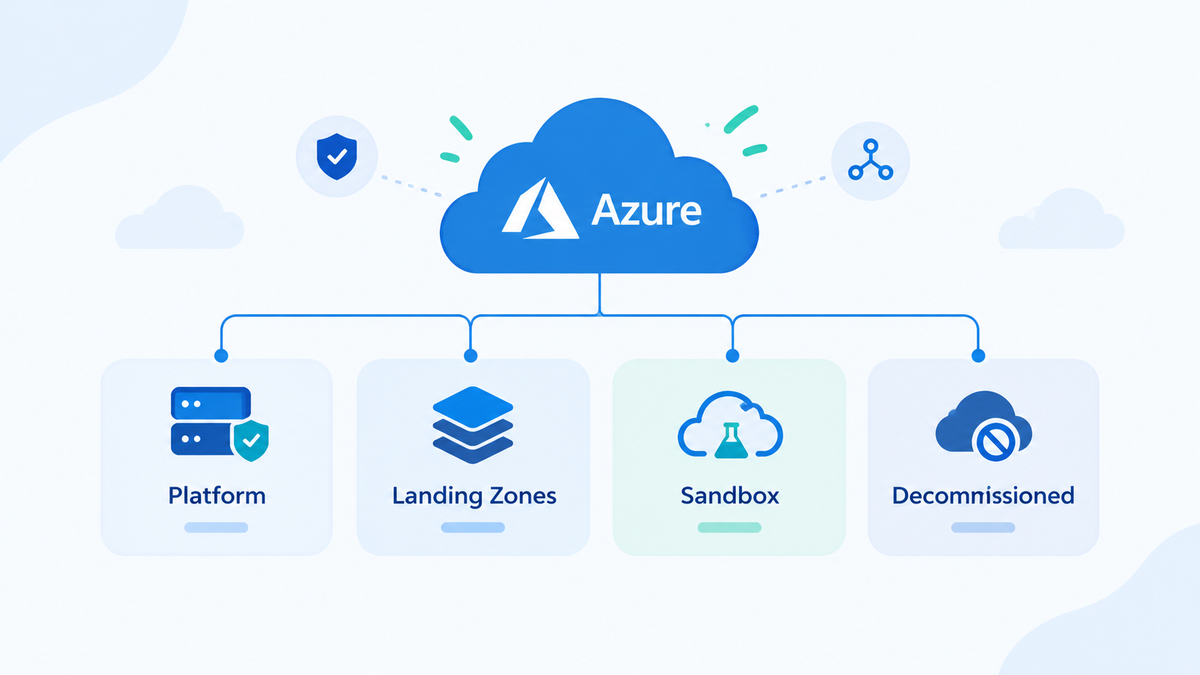
Management group hierarchy
Management groups apply policy and access to many subscriptions at once. Microsoft's reference hierarchy includes:
|
Management group |
Purpose |
|---|---|
|
Platform |
Parent for Security, Management, Connectivity and Identity, each with its own subscription |
|
Landing zones: Corp |
Workloads that need connectivity to the corporate network through the hub |
|
Landing zones: Online |
Workloads that need direct internet access or no virtual network |
|
Landing zones: Local |
Azure Local clusters, which have different policy needs |
|
Sandbox |
Isolated testing and exploration with less restrictive policies |
|
Decommissioned |
Canceled landing zones, which Azure deletes after 30 to 60 days |
You do not need every level on day one. Adding a management group later is easy; restructuring subscriptions later is not.
Network
Most organizations use hub and spoke: a hub virtual network in the connectivity subscription holds Azure Firewall, VPN Gateway or ExpressRoute, Azure Bastion and DNS Private Resolver, and workload virtual networks peer to it as spokes. Azure Virtual WAN suits large multi-region estates with many branches. Plan IP address ranges with room to grow, because overlapping ranges with on-premises networks are among the hardest problems to fix in production.
Identity and policy
Microsoft Entra ID is the identity backbone, with role-based access control, Privileged Identity Management for just-in-time admin access, and Conditional Access. Microsoft recommends two or more emergency access accounts so a misconfigured policy cannot lock everyone out. Azure Policy enforces guardrails such as allowed regions, required tags, encryption and diagnostic settings. Start with Microsoft's built-in initiatives and add custom policies only for real gaps, and give every exemption an owner and an expiry date.
Choosing regions comes first, because network and policy decisions depend on it. See our guide to Azure regions and data residency for US companies.
Benefits of an Azure Landing Zone
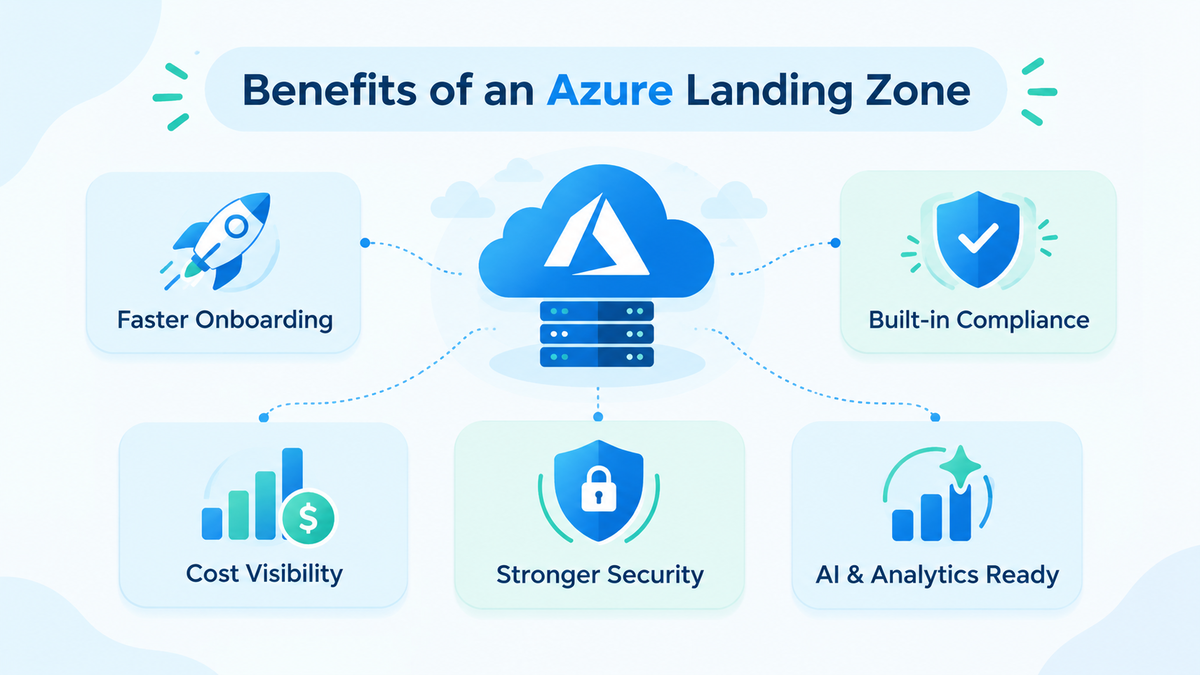
1. Faster, safer onboarding
New workloads get a pre-approved subscription, network and permissions instead of a fresh design debate.
2. Compliance by default
Azure Policy and Microsoft Defender for Cloud turn audit evidence into a compliance report rather than a folder of screenshots.
3. Cost visibility
Enforced tagging, budgets and alerts make spend attributable to teams and catch drift while it is small.
4. Smaller blast radius
Segmented networks and least-privilege access limit how far a mistake or compromised credential can reach.
5. A base for AI and analytics
Fabric, Power BI and Copilot depend on clean identity and permissions. Copilot surfaces whatever a user can already access, so permission hygiene is a prerequisite.
Challenges and Common Mistakes
|
Mistake |
How to avoid it |
|---|---|
|
Rushing discovery |
The hardest decisions to reverse are made here; give it real time |
|
Poor IP planning |
Allocate address space with headroom and avoid overlap with on-premises |
|
Too many custom policies |
Start with built-in initiatives; add custom policy only for genuine gaps |
|
Cost management left for later |
Set tags, budgets and alerts on day one |
|
Broad permissions |
Apply least privilege from the start; it is harder to remove access than to withhold it |
|
Manual portal changes |
Deploy and change the platform through infrastructure as code |
|
Naming and tagging decided late |
Agree standards in the first week; they cannot practically be changed across a live estate |
The most common non-technical delay is getting decisions from stakeholders with competing views on subscription ownership and network design. Hold those conversations early.
Tools and Deployment Options
Microsoft's implementation options recommend infrastructure as code with Azure Verified Modules (AVM), which Microsoft describes as "reusable, customizable, and extensible building blocks to build a platform landing zone with Bicep or Terraform."
|
Approach |
Best for |
|---|---|
|
Accelerator with AVM for Bicep (recommended IaC path) |
Azure-only estates and teams familiar with ARM and Bicep; no state file to manage |
|
Accelerator with AVM for Terraform (recommended IaC path) |
Multi-cloud estates and teams with existing Terraform practice |
|
Azure portal accelerator |
Organizations without infrastructure as code expertise that want a working foundation quickly |
|
Custom implementation |
Rare; only when the accelerators cannot meet a specific requirement |
If your reference material predates Azure Verified Modules, it describes an older approach. Pick the language your team can maintain.
How to Build an Azure Landing Zone?
-
Define requirements: workloads in scope, compliance obligations (for example HIPAA, SOC 2, ISO 27001, NIST, FedRAMP for federal work), target regions and team structure.
-
Design the management group hierarchy and decide which policies apply at which level.
-
Set up identity: Conditional Access, Privileged Identity Management, emergency access accounts and hybrid sync if needed.
-
Design the network: hub, address space, firewall, spoke peering, private DNS and on-premises connectivity.
-
Implement governance: assign built-in policy initiatives, add custom policies for gaps, configure remediation.
-
Configure cost management: budgets with alerts, an enforced tagging standard and cost allocation rules.
-
Deploy monitoring: central Log Analytics, diagnostic settings by policy, Defender for Cloud, alerts and backup.
-
Onboard the first workload landing zone and write the runbook as you go.
-
Automate everything with the AVM accelerator so changes go through review and the platform can be rebuilt from code.
A landing zone is one step in the Ready phase of planning Azure cloud adoption, and the workloads you place in it should follow Azure architecture best practices.
For how the landing zone fits into a wider move to Azure, see how to plan an Azure migration and Azure migration cost and timeline.
How to Measure Success?
|
Area |
KPI |
What it shows |
|---|---|---|
|
Security |
Defender for Cloud Secure Score |
Overall security posture trend |
|
Governance |
Azure Policy compliance rate |
How many resources meet your guardrails |
|
Identity |
MFA coverage on privileged accounts; standing admin assignments |
Exposure from privileged access |
|
Cost |
Untagged resource rate; budget variance |
Whether spend is attributable and controlled |
|
Operations |
Time to onboard a new subscription; changes deployed through pipelines |
How well the platform supports teams |
Agree targets for each KPI before go-live, so they work as engineering standards rather than blame after an incident.
Frequently Asked Questions
What is a landing zone in Azure?
It is a pre-configured, governed Azure environment, made of a platform landing zone and workload landing zones, that sets identity, networking, policy, cost and monitoring standards before workloads are deployed.
What does landing zone mean in cloud computing?
In cloud computing, a landing zone is a ready-to-use, secure and governed foundation of accounts or subscriptions, networking and policies that new workloads are deployed into.
What is the difference between AWS Control Tower and Azure landing zones?
AWS Control Tower is an AWS service that sets up and governs a multi-account AWS environment. Azure landing zones are a reference architecture from Microsoft's Cloud Adoption Framework, deployed with accelerators and Azure Verified Modules across management groups and subscriptions.
Do I need a landing zone before migrating to Azure?
Yes, ideally. Without one, migrated workloads land in an ungoverned environment that later needs rework. A simplified landing zone can be built first and expanded over time.
Can I add a landing zone to an existing Azure environment?
Yes. A retrofit is harder than a new build because subscriptions, networks and permissions already exist, but it is bounded work and usually cheaper than continuing without governance.
Build the Foundation Before the Workloads
An Azure landing zone turns Azure from a collection of subscriptions into a governed platform. Settle the environment design areas early, enforce guardrails with policy, deploy with Azure Verified Modules, and onboard workloads into a structure that scales.